 Finowl
Password breach checks · Dating apps
Breached password checks for dating app signups
A dating account protects photos, conversations and details members may never share anywhere else. Yet many people sign up quickly, on a phone, with a password they already use. Screening that password against breach data at signup and reset keeps known-compromised values out and makes credential stuffing against your login far less productive.
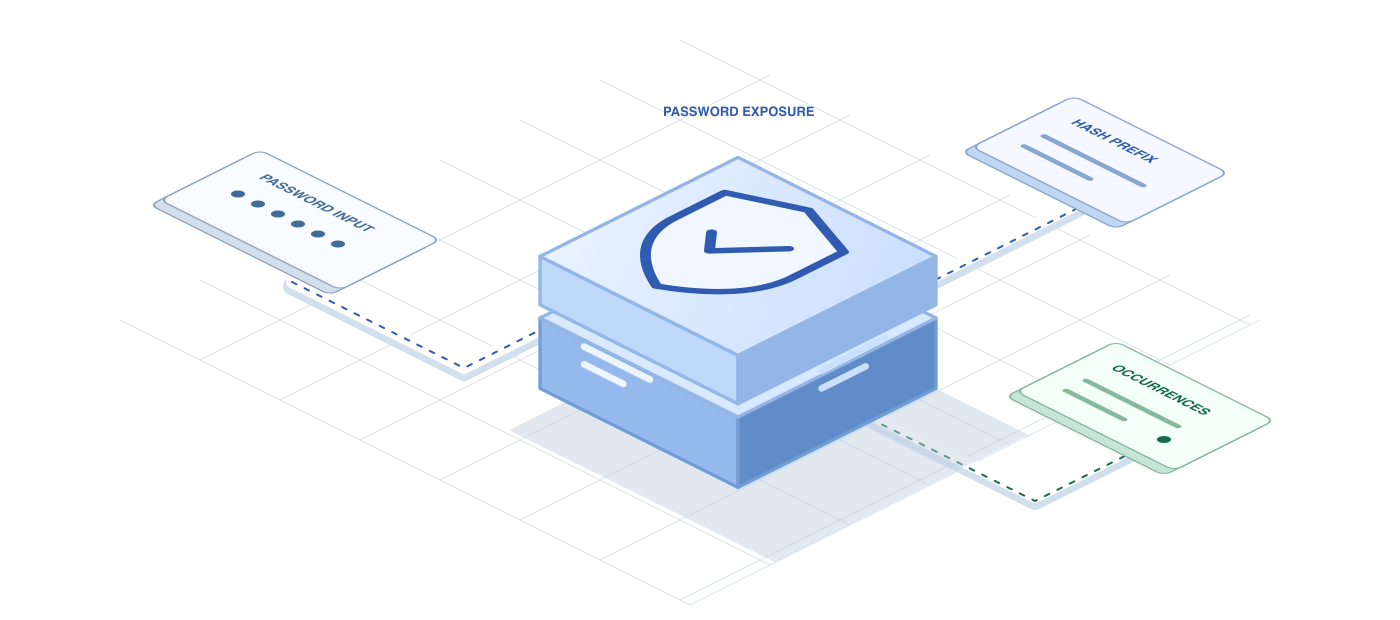
The Finowl password breach API returns a breached flag and a count. Finowl hashes the password with SHA-1 and looks up only a five-character prefix of that hash using a padded range search, and the password is never logged, stored or returned. For an app that handles intimate data, that privacy design is as important as the check itself.
USE CASES
Where it fits in dating apps
Mobile signup screening
Check the password during mobile onboarding and show a short inline note if it is breached, keeping the member’s other answers so they can fix it without starting over.
Reset after suspicious activity
When your safety team forces a reset after a suspected takeover, require a new password that passes the breach check so the attacker cannot return with the same credential.
Email and password login option
Apps that offer social and phone sign-in alongside email and password can apply the check only to the password path, adding protection exactly where reused credentials appear.
Moderator and support accounts
Staff who review reports can see private messages and photos. Screen their passwords too, since a compromised internal account would expose many members at once.
HOW TO INTEGRATE
The workflow
- 1
Send the password from your API server to POST /v1/breaches/password, never from the mobile app with your key.
- 2
If breached is true, return a short validation message to the onboarding screen.
- 3
If breached is false, continue onboarding under your normal password rules.
- 4
Exclude password fields from mobile analytics, crash reporting and server logs.
- 5
Fall back to your standard rules if the API times out, without retrying the same request.
curl https://api.finowl.co/v1/breaches/password \
  -H "Authorization: Bearer $FINOWL_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{
  "password": "correct-horse-battery-staple"
}'
Returns breached and count. Finowl processes the password transiently and never logs, stores or returns it. 1 credit per check.
GOOD PRACTICE
Before you ship
Mobile apps can be decompiled, so never ship your API key in the app. Route checks through your backend and return only the accept or reject result.
Onboarding drop-off is costly on mobile. Keep rejection copy to one friendly line and suggest a passphrase or a password manager to reduce repeated failures.
Audit mobile analytics and crash reporting SDKs to make sure password fields are masked, so the value never leaves the device through a side channel.
Read the API reference for every field and error code. Each lookup costs 1 credit; see pricing.
A FEW GOOD QUESTIONS
Common questions
More for dating apps
Breached password checks for dating app signups
Start with 100 free credits every month and test the request above in the sandbox.