 Finowl
Password breach checks · Gaming
Breached password checks for player registration
Players often reuse a password they first created for another game, a forum or a launcher. If that password is in breach data, your title inherits the risk the moment they register. The Finowl password breach API returns whether the password has been seen and how many times, so your registration and reset forms can ask for another one.
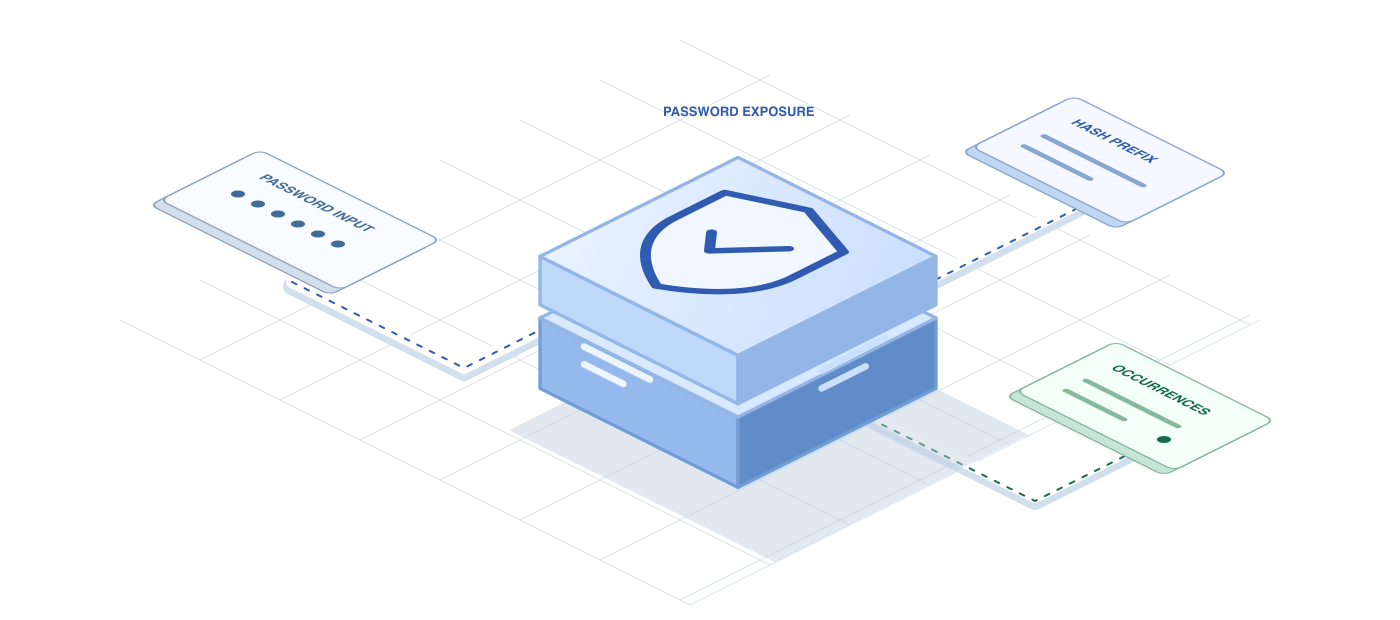
The check is built to respect the sensitivity of the value. Finowl hashes the password with SHA-1 and looks up only a five-character hash prefix with padding, processing the password transiently without logging, storing or returning it. Your game backend receives a simple breached flag and count to act on.
USE CASES
Where it fits in gaming
Account creation in the launcher
Check the password during registration in your launcher or website and show an inline prompt if it is breached, before the player links platforms or makes a first purchase.
Recovery after a takeover
When support restores a hijacked account, require the player to set a new password that passes the breach check, so the attacker’s known credential stops working for good.
Parent and family accounts
Family accounts often control purchases and parental settings. Screening those passwords protects payment methods and controls that matter to every household playing your game together.
Community and creator tools
Apply the check to logins for modding portals, creator dashboards or community tools that can publish content to many players, where a compromised account could spread scams.
HOW TO INTEGRATE
The workflow
- 1
Call POST /v1/breaches/password from your account backend when a player submits a new password.
- 2
Show a short in-game or web message if breached is true, inviting the player to pick something longer and unique.
- 3
Continue registration normally when breached is false.
- 4
Make sure password fields never reach telemetry, crash reports or analytics pipelines.
curl https://api.finowl.co/v1/breaches/password \
  -H "Authorization: Bearer $FINOWL_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{
  "password": "correct-horse-battery-staple"
}'
Returns breached and count. The password is hashed and only a short prefix is used for the lookup. 1 credit per check.
GOOD PRACTICE
Before you ship
Game clients ship to players, so never embed your API key in a client build. Call Finowl only from your servers and expose a minimal result to the client.
Telemetry and crash reporting can capture form data in unexpected ways. Audit those pipelines so passwords never leave the account service in any form.
Keep messages friendly and short, especially in console flows where typing is slow. Suggesting a passphrase helps players succeed on the next attempt.
Read the API reference for every field and error code. Each lookup costs 1 credit; see pricing.
A FEW GOOD QUESTIONS
Common questions
More for gaming
Breached password checks for player registration
Start with 100 free credits every month and test the request above in the sandbox.