 Finowl
Password breach checks · Marketplaces
Breached password checks for buyer and seller accounts
Seller accounts on a marketplace are small businesses, often run by one person who reuses a password across shipping tools, email and the platform itself. Screening passwords against breach data at signup and reset closes one of the easiest doors attackers use to hijack those accounts and quietly redirect earnings.
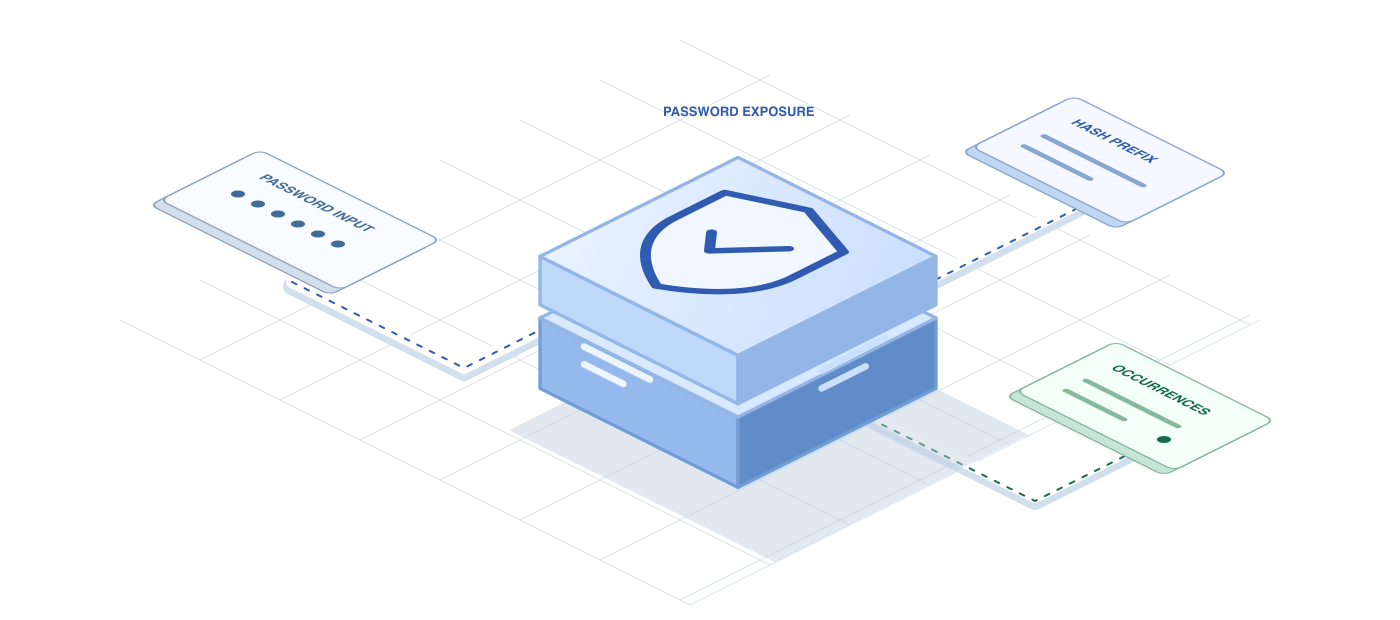
The Finowl password breach API returns whether a password has been seen in breach data and how often. It works through a padded k-anonymity range search on a short SHA-1 hash prefix, and the password is never logged, stored or returned, which keeps the check consistent with how carefully you already treat seller credentials.
USE CASES
Where it fits in marketplaces
Seller registration
Screen the password when a new seller creates their shop, before they link a payout account, so the account that will receive money starts with a credential not in breach data.
Buyer signup and reset
Apply the same check to buyer registration and password resets, protecting stored payment methods and order history without adding steps for buyers who choose a fresh password.
Post-incident recovery
After your team recovers a hijacked seller account, require a new password that passes the breach check so the attacker cannot simply log back in with a known value.
Team members on shop accounts
Some sellers add staff to help manage listings. Screen passwords for those sub-accounts too, since they can often edit listings and respond to buyer messages.
HOW TO INTEGRATE
The workflow
- 1
Route password submissions from signup, reset and recovery to a backend handler that calls POST /v1/breaches/password.
- 2
When breached is true, ask for a different password with a short explanation.
- 3
When breached is false, continue with your existing password rules and complete the flow.
- 4
Exclude password fields from logs, analytics events and support tool exports.
- 5
Track how often passwords are rejected to understand the impact on onboarding completion.
curl https://api.finowl.co/v1/breaches/password \
  -H "Authorization: Bearer $FINOWL_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{
  "password": "correct-horse-battery-staple"
}'
Returns breached and count. A count of 0 means the password was not found in breach data. Each check costs 1 credit.
GOOD PRACTICE
Before you ship
Recovered accounts are high risk. Always run the check when a seller sets a new password after a takeover, and pair it with a prompt to enable multi-factor authentication.
Sellers are busy. Keep rejection messages to a single clear sentence, and suggest a password manager instead of a list of complexity requirements.
If Finowl returns a timeout or 5xx error, accept the password under your normal rules. The lookup may have been charged, so avoid automatic retries.
Read the API reference for every field and error code. Each lookup costs 1 credit; see pricing.
A FEW GOOD QUESTIONS
Common questions
More for marketplaces
Breached password checks for buyer and seller accounts
Start with 100 free credits every month and test the request above in the sandbox.