 Finowl
Password breach checks · Media and publishing
Breached password checks for news and media subscriptions
Many readers choose a quick password when they hit a paywall, often one they already use elsewhere. Those reused passwords are exactly what credential stuffing tools test against subscription logins. Checking each new or changed password against breach data, as NIST SP 800-63B recommends, keeps the most common leaked values out of your subscriber base. Finowl returns whether the password has been seen and how often.
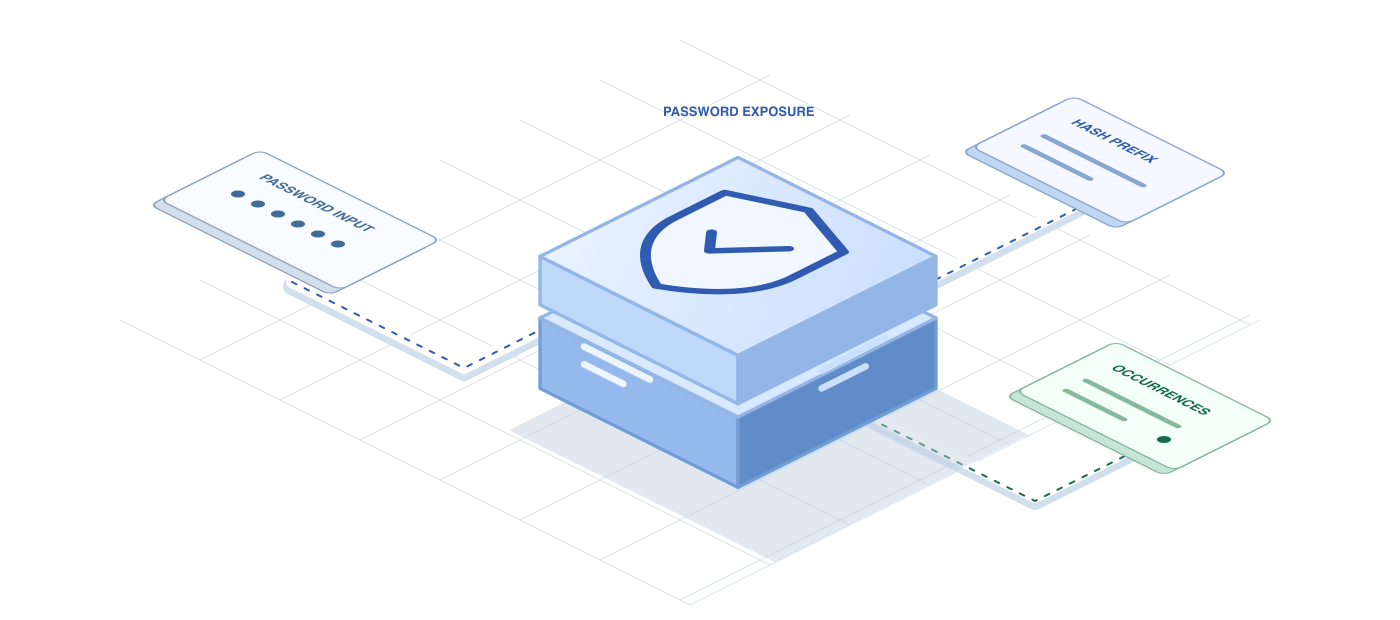
The check is private by design. Finowl hashes the password with SHA-1 and looks up only a 5-character hash prefix through a padded k-anonymity range search. The password is processed transiently and never logged, stored or returned. That lets publishers strengthen subscriber security without adding risky data flows to a stack that already includes many third-party scripts.
USE CASES
Where it fits in media and publishing
Paywall registration
When a reader registers or subscribes at the paywall, reject passwords that appear in breach data and suggest a passphrase, keeping checkout short while closing an easy door for attackers.
Background login checks
After login, check the password server side and prompt the subscriber to update it on their next visit if it appears in breach data, without interrupting the article they opened.
Contributor and editor accounts
Require that editors, freelancers and contributors with content management access use passwords not found in breach data, since a compromised editor login could publish false content.
Bulk reset after stuffing waves
After a detected credential stuffing attack, check passwords at each subscriber's next login and require a reset where the current password appears in breach data.
HOW TO INTEGRATE
The workflow
- 1
Route new and changed passwords from your subscription service to POST /v1/breaches/password on the server.
- 2
Block or warn based on breached and count, with stricter thresholds for editor and admin accounts.
- 3
Return a short, plain message asking for a different password without revealing the count.
- 4
On errors, fall back to local rules so registration and checkout keep working.
curl https://api.finowl.co/v1/breaches/password \
  -H "Authorization: Bearer $FINOWL_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{
  "password": "correct-horse-battery-staple"
}'
Runs when a reader subscribes at the paywall. A breached result asks for a different password before the subscription account is created.
GOOD PRACTICE
Before you ship
Publishing sites run many third-party scripts. Make sure password fields are excluded from analytics, session replay and tag managers as well as server logs.
Use stricter rules for newsroom accounts. Editors and contributors with publishing rights warrant blocking any breached password, regardless of count.
Avoid checkout abandonment. If the check fails, let the subscription proceed under local rules and recheck the password at the next login.
Read the API reference for every field and error code. Each lookup costs 1 credit; see pricing.
A FEW GOOD QUESTIONS
Common questions
More for media and publishing
Breached password checks for news and media subscriptions
Start with 100 free credits every month and test the request above in the sandbox.